
4YFN Barcelona 2026
Not a showcase of prototypes
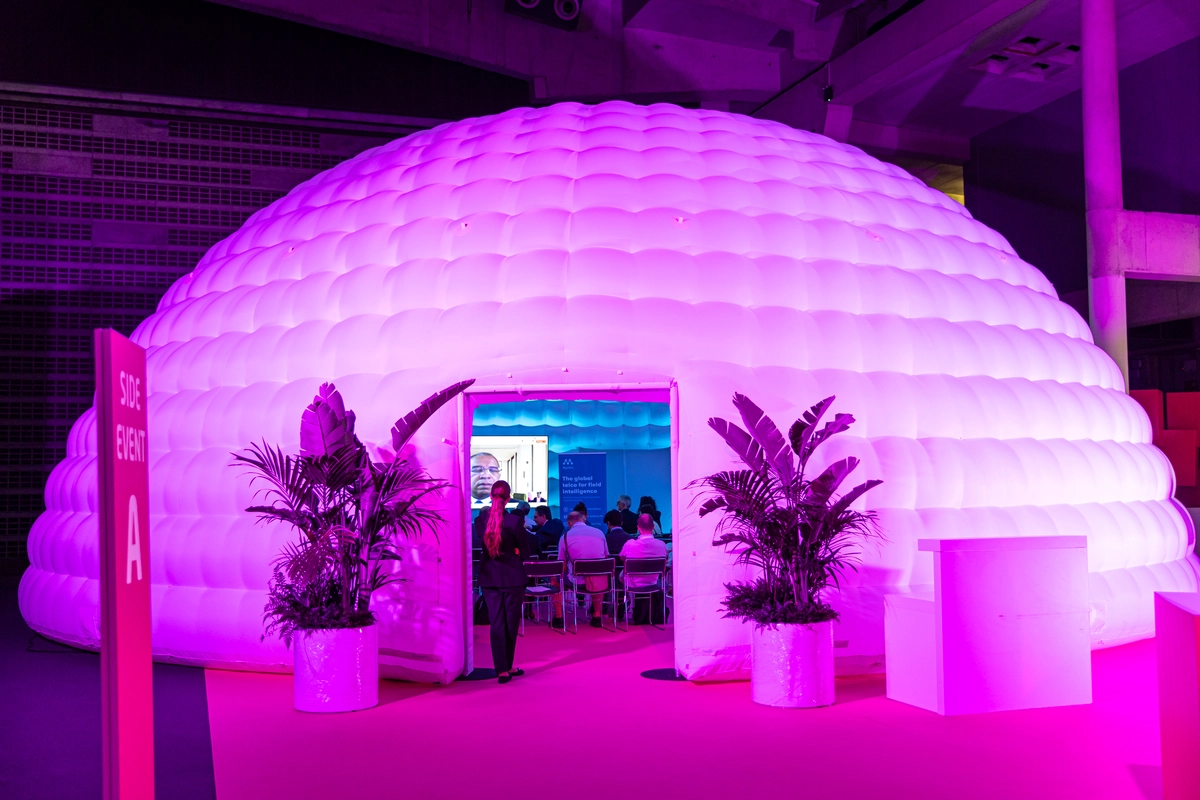
Thinger.io took part in 4YFN Barcelona 2026, the international innovation event held within the framework of the Mobile World Congress, from March 2 to 5, 2026, in Barcelona.
4YFN brings together technology startups, corporations, industrial integrators and investors who are building the digital infrastructure of the coming years.
It is not a showcase of prototypes, but a space where real architectures, cybersecurity, regulatory compliance and production-ready deployments are discussed.
In this environment, the conversation no longer revolves solely around launching products or connecting devices, but around how to scale technological solutions securely, comply with increasingly demanding regulatory frameworks and ensure operational continuity across distributed infrastructures.
Discussions focus on applied cybersecurity, data protection, resilience and integration with corporate systems. They also address how to move from pilot projects to real-world operations without compromising technical control.
Past event
4YFN Barcelona 2026
- When
- Where
- Hall 8.1, Barcelona
- Stand
- 8.1B45.4A
- Framework
- Mobile World Congress
- Exhibitor
- ThinRemote.ioStartup
Thinger.io officially presented ThinRemote.io, its new vertical for secure remote access.
This event has taken place.
The launch
ThinRemote.io, presented at 4YFN
In this context, we officially presented ThinRemote.io, the new strategic vertical of Thinger.io focused on secure remote access.
ThinRemote.io is built for industrial, edge and any distributed infrastructure requiring controlled remote connectivity. It emerges as a natural response to a need that is already on the table: organizations need to intervene in distributed systems without compromising their architecture or increasing the risk surface.

The foundation
Years of operation in real industrial environments
Thinger.io provides a solid infrastructure with years of operation in real industrial environments, where scalability, security and control are structural requirements.
In 2026, we set out to complete the ISO/IEC 27001 certification process. This milestone consolidates a model based on risk management, asset control and continuous improvement.
Update: Thinger.io achieved ISO/IEC 27001:2022 certification in September 2026. Read what the certification covers.
The problem
Why has secure remote access become critical in production IoT?
In mature IoT deployments, collecting data is no longer the primary challenge.
The real complexity appears when teams need to intervene, diagnose and resolve incidents remotely without exposing the network or increasing operational risk. As infrastructures become geographically distributed and regulatory pressure grows, remote access is no longer a secondary tool. It becomes a core architectural concern.

Many organizations still rely on legacy VPNs, manual port exposure or generic remote desktop tools that were never designed for large-scale industrial environments. This creates:
- unnecessary attack surfaces;
- fragmented access control;
- limited visibility into who accesses what and when.
How it works
How does ThinRemote.io reach distributed devices safely?
ThinRemote.io is designed for industrial devices, edge gateways, PLCs, HMIs, embedded systems and any technical equipment operating within distributed infrastructures.
Exposing inbound services
- Ports opened on the site
- Complex VPN infrastructures to deploy
- Access control fragmented across tools
Secure outbound connections
- The device connects out to the platform
- Access managed and authenticated centrally
- Every access fully traceable
No open ports, no VPN
Instead of exposing inbound services, devices establish secure outbound connections to the platform. This eliminates the need to open ports or deploy complex VPN infrastructures. The platform centrally manages and authenticates access, making it fully traceable and enabling organizations to maintain control while reducing operational complexity.
ThinRemote.io does not replace existing platforms. It complements them by adding a secure intervention layer to environments that already manage data, operations or distributed processes.

Agent
Web console
Command line tool
With Thinger.io
From monitoring to auditable resolution
When integrated, Thinger.io and ThinRemote.io enable a complete operational flow.
Monitoring
Anomaly detection
Secure remote intervention
Auditable resolution
Organizations can also deploy ThinRemote.io independently in other sectors, where secure remote access is a critical requirement within a controlled and scalable architecture. The ThinRemote page explains how it relates to Thinger.io.
Let's talk
Continue the conversation
4YFN is over, but the conversation goes on.
If you work in industrial IoT, edge computing or distributed technical support, we would love to connect.
Secure remote access for your distributed devices
Reach industrial devices, edge gateways and embedded systems over an outbound connection, with no open ports and no VPN.